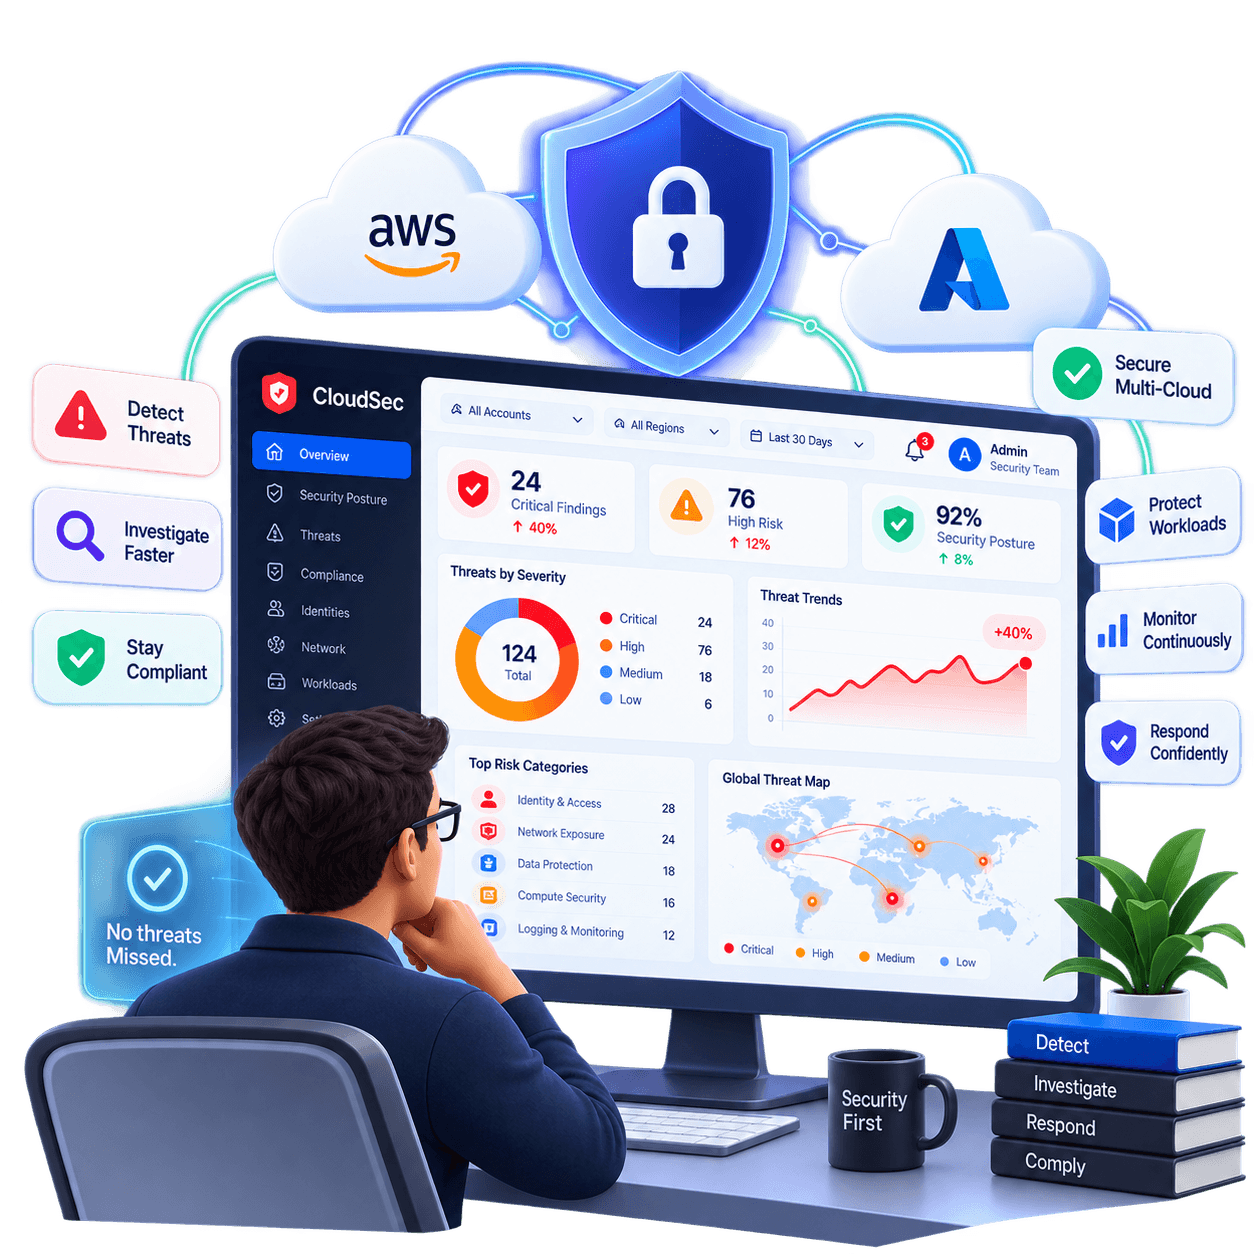
Know your security posture
before an attacker does.

CloudSec continuously audits AWS and Azure environments, scores security posture, and identifies which misconfigurations to fix first. No agents, no write permissions.

CloudSec CSPM Platform 3D Illustration

The Problem

Security drift happens continuously. Audits happen quarterly.

Developers deploy daily across AWS accounts and Azure subscriptions. A single modified security group, overpermissive IAM role, or unencrypted storage bucket creates an attack chain that perimeter tools miss. Security teams need unified posture scores and graph-based attack paths to eliminate real risk.

×

Security visibility fragmented across AWS Security Hub and Azure Defender consoles

×

Alert fatigue from thousands of misconfigurations with no contextual exploitability ranking

×

Invisible attack chains combining multiple low-severity issues into critical exposures

×

Audit fire drills requiring weeks of manual evidence gathering for SOC 2, CIS, and HIPAA

The Promise

“Know your cloud's security posture before an attacker does.”
STAGE 01

CLOUDSEC · CSPM POSTURE

One Posture Score Across Clouds.

Composite weighted severity scoring and 30-day security trends across every connected AWS account and Azure subscription.

Cloudsec
CloudSec — Composite Posture Score
Posture Score
Continuous Audit
Attack Path
Compliance

Read-only agentless scanning · 14 AWS accounts & 8 Azure subscriptions

82CSPM
Multi-Cloud Security Posture30d trend: +6 pts
Passed Checks: 1420
Medium / Low: 380
Critical / High: 178

Connected Cloud Accounts & Subscriptions

aws-prod-paymentsAWS2 Critical94%
azure-sub-productionAzure6 High81%
aws-core-platformAWS11 Critical76%
Critical Findings
23
↑ -8 this week
Coverage
98.4%
↑ AWS + Azure
Worst Service
Azure NSG
↓ drift detected
STAGE 02

CLOUDSEC · CONTINUOUS AUDITING

Auditing, Not a Quarterly Checklist.

Agentless scans detect security drift, open ports, permission escalations, and newly exposed assets in real time across AWS and Azure.

Cloudsec
CloudSec — Continuous Auditing & Resource Watch
Posture Score
Continuous Audit
Attack Path
Compliance

Real-time drift detection · Agentless read-only auditing across AWS and Azure

Audited Checks
1,978
↑ passed 94.2%
Drift Events
4
▲ in last 1 hour
Auto-Remediated
18
↑ safe guardrails
Real-Time Resource Watch StreamLive Sync Active
S3 Bucket Public Read DriftCritical
s3://customer-invoices-2026 · aws-core-platform
2m ago
Overprivileged IAM Role AssumedHigh
role/PaymentProcessorServiceRole · aws-prod-payments
9m ago
Unrestricted Security Group 0.0.0.0/0Critical
sg-09a8f21e (Port 22 Open) · aws-core-platform
14m ago
Agentless event streams active
Drift rate: 0.2/hr
STAGE 03

CLOUDSEC · ATTACK PATH & THREAT MAP

See the Path an Attacker Takes.

Graph-based attack path visualization maps chains from internet entry points to critical cloud databases and sensitive workloads.

Cloudsec
CloudSec — Attack Path & Threat Map
Posture Score
Continuous Audit
Attack Path
Compliance

3-hop exploitable chain discovered · Internet → RDS Production Database

Critical Attack Path #1 (Exploitable Chain)

Internet ingress chains with IMDSv1 token exposure to compromise database

High Exploitability
Attack path blast radius modeled
STAGE 04

CLOUDSEC · CONTINUOUS COMPLIANCE

Turn Findings into Audit Evidence.

Maps security findings continuously to CIS, SOC 2, ISO 27001, PCI-DSS, NIST, and HIPAA frameworks with exportable board reports.

Cloudsec
CloudSec — Compliance & Audit Evidence
Posture Score
Continuous Audit
Attack Path
Compliance

Framework scoring across AWS and Azure · Exportable board-ready audit packages

Frameworks
5
→ CIS, SOC 2, PCI, ISO, HIPAA
Audit Readiness
91.2%
↑ blended score
Evidence Packs
12
↑ exported last 30d

Framework Alignment & Automated Evidence
CIS AWS Benchmark v2.094%
152/162 controls verified
SOC 2 Type II (Security & Availability)92%
78/85 controls verified
ISO 27001:2022 ISMS Controls96%
90/94 controls verified
Continuous auditor export ready

Core Capabilities

Continuous CSPM for AWS and Azure.

Composite CSPM posture scoring

Continuous agentless auditing for AWS & Azure

Resource Watch real-time drift detection

Graph-based attack-path visualization

Global threat & exposure mapping

CIS, SOC 2, ISO 27001 & HIPAA compliance

CloudSecWorkflow Architecture

CloudSec workflow.

↺ CONTINUOUS POSTURE: RE-SCAN & VERIFY POSTURECLOUD ENVIRONMENTresourcesCompute · Storage · DBsAWS & Azure AssetsidentitiesIAM · Entra ID · KeysEntitlement Boundary02 · INGESTSECURITYSIGNALSConfig Drift AlertsOpen Ports & CVEs03 · GRAPHrelationshipsCONTEXTMulti-Cloud Meshattack pathInternet → WorkloadChained Exploit Pathblast radiusLateral Impact ScopeSensitive Data Reach05 · SCORINGPRIORITIZEDRISKReal ExploitabilityTop 2% Focus06 · DEFENSEISOLATE /PROTECT ↺1-Click IsolationVerify Posture ↺

Attack Path Analysis

04A · CHAIN SIMULATION

Simulates how an external adversary could traverse from internet entry points through permissions to reach sensitive workloads.

Internet to Workload Chain
Privilege Escalation Routes
Lateral Movement Traversal
Critical Data Reachability
CloudSec Product Overview
Agentless Multi-Cloud CSPM (AWS + Azure)Continuous Posture & Compliance AuditingLeast Privilege IAM Analysis & Zero Plaintext
Core MissionThe CloudSec Purpose

Isolate risk before it becomes an incident.

I continuously watch your cloud environment, expose security risks, and show you where an attack could travel before it becomes a problem.
CloudSec/ CSPM & Attack Path Intelligence